ConfigJanitor - Kubernetes unused ConfigMap and Secret cleaner
Deletes ConfigMaps and Secrets no pod references and reports the cleanup on Slack.


Standardize provisioning and Day 2 operations with less risk and operational overhead. Get full visibility and control across all infrastructure workflows.


Our goal is for Kestra to become the go-to solution across the organization whenever data wrangling and complex pipeline orchestration are needed.
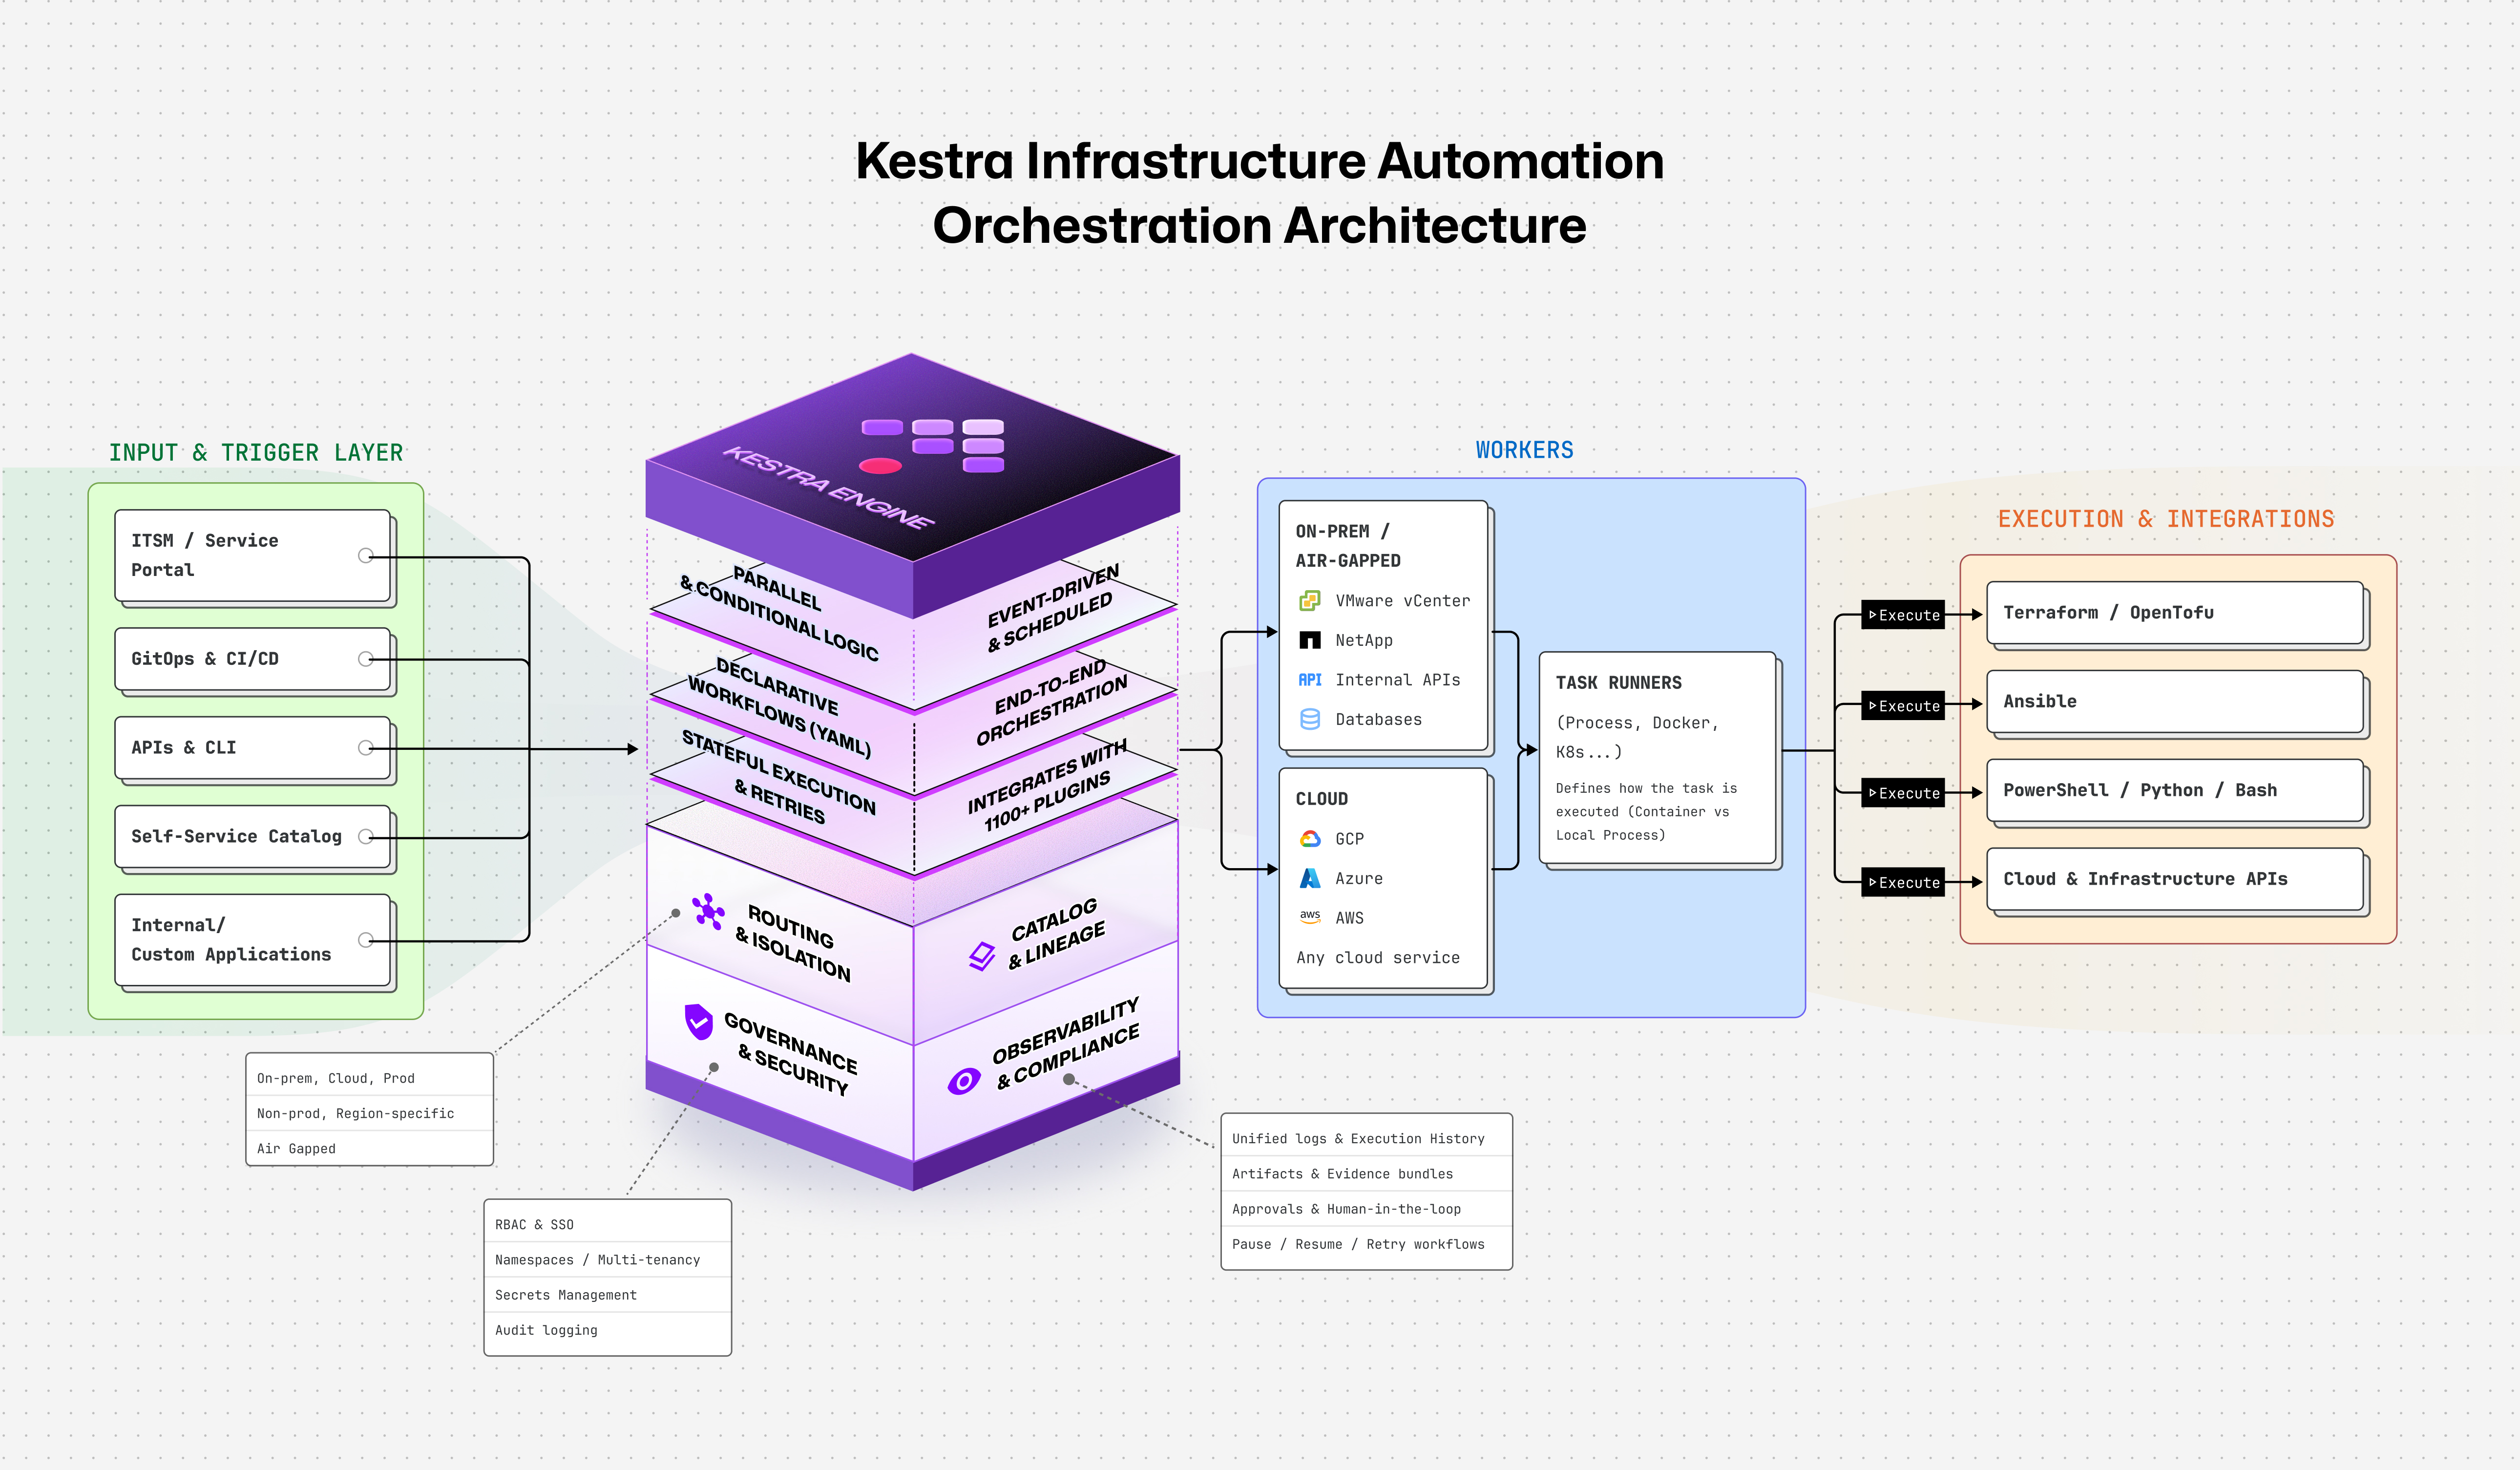
Run IaC the same way every time. Kestra orchestrates the full lifecycle with shared parameters, secrets, retries, and evidence-grade logs across all environments.
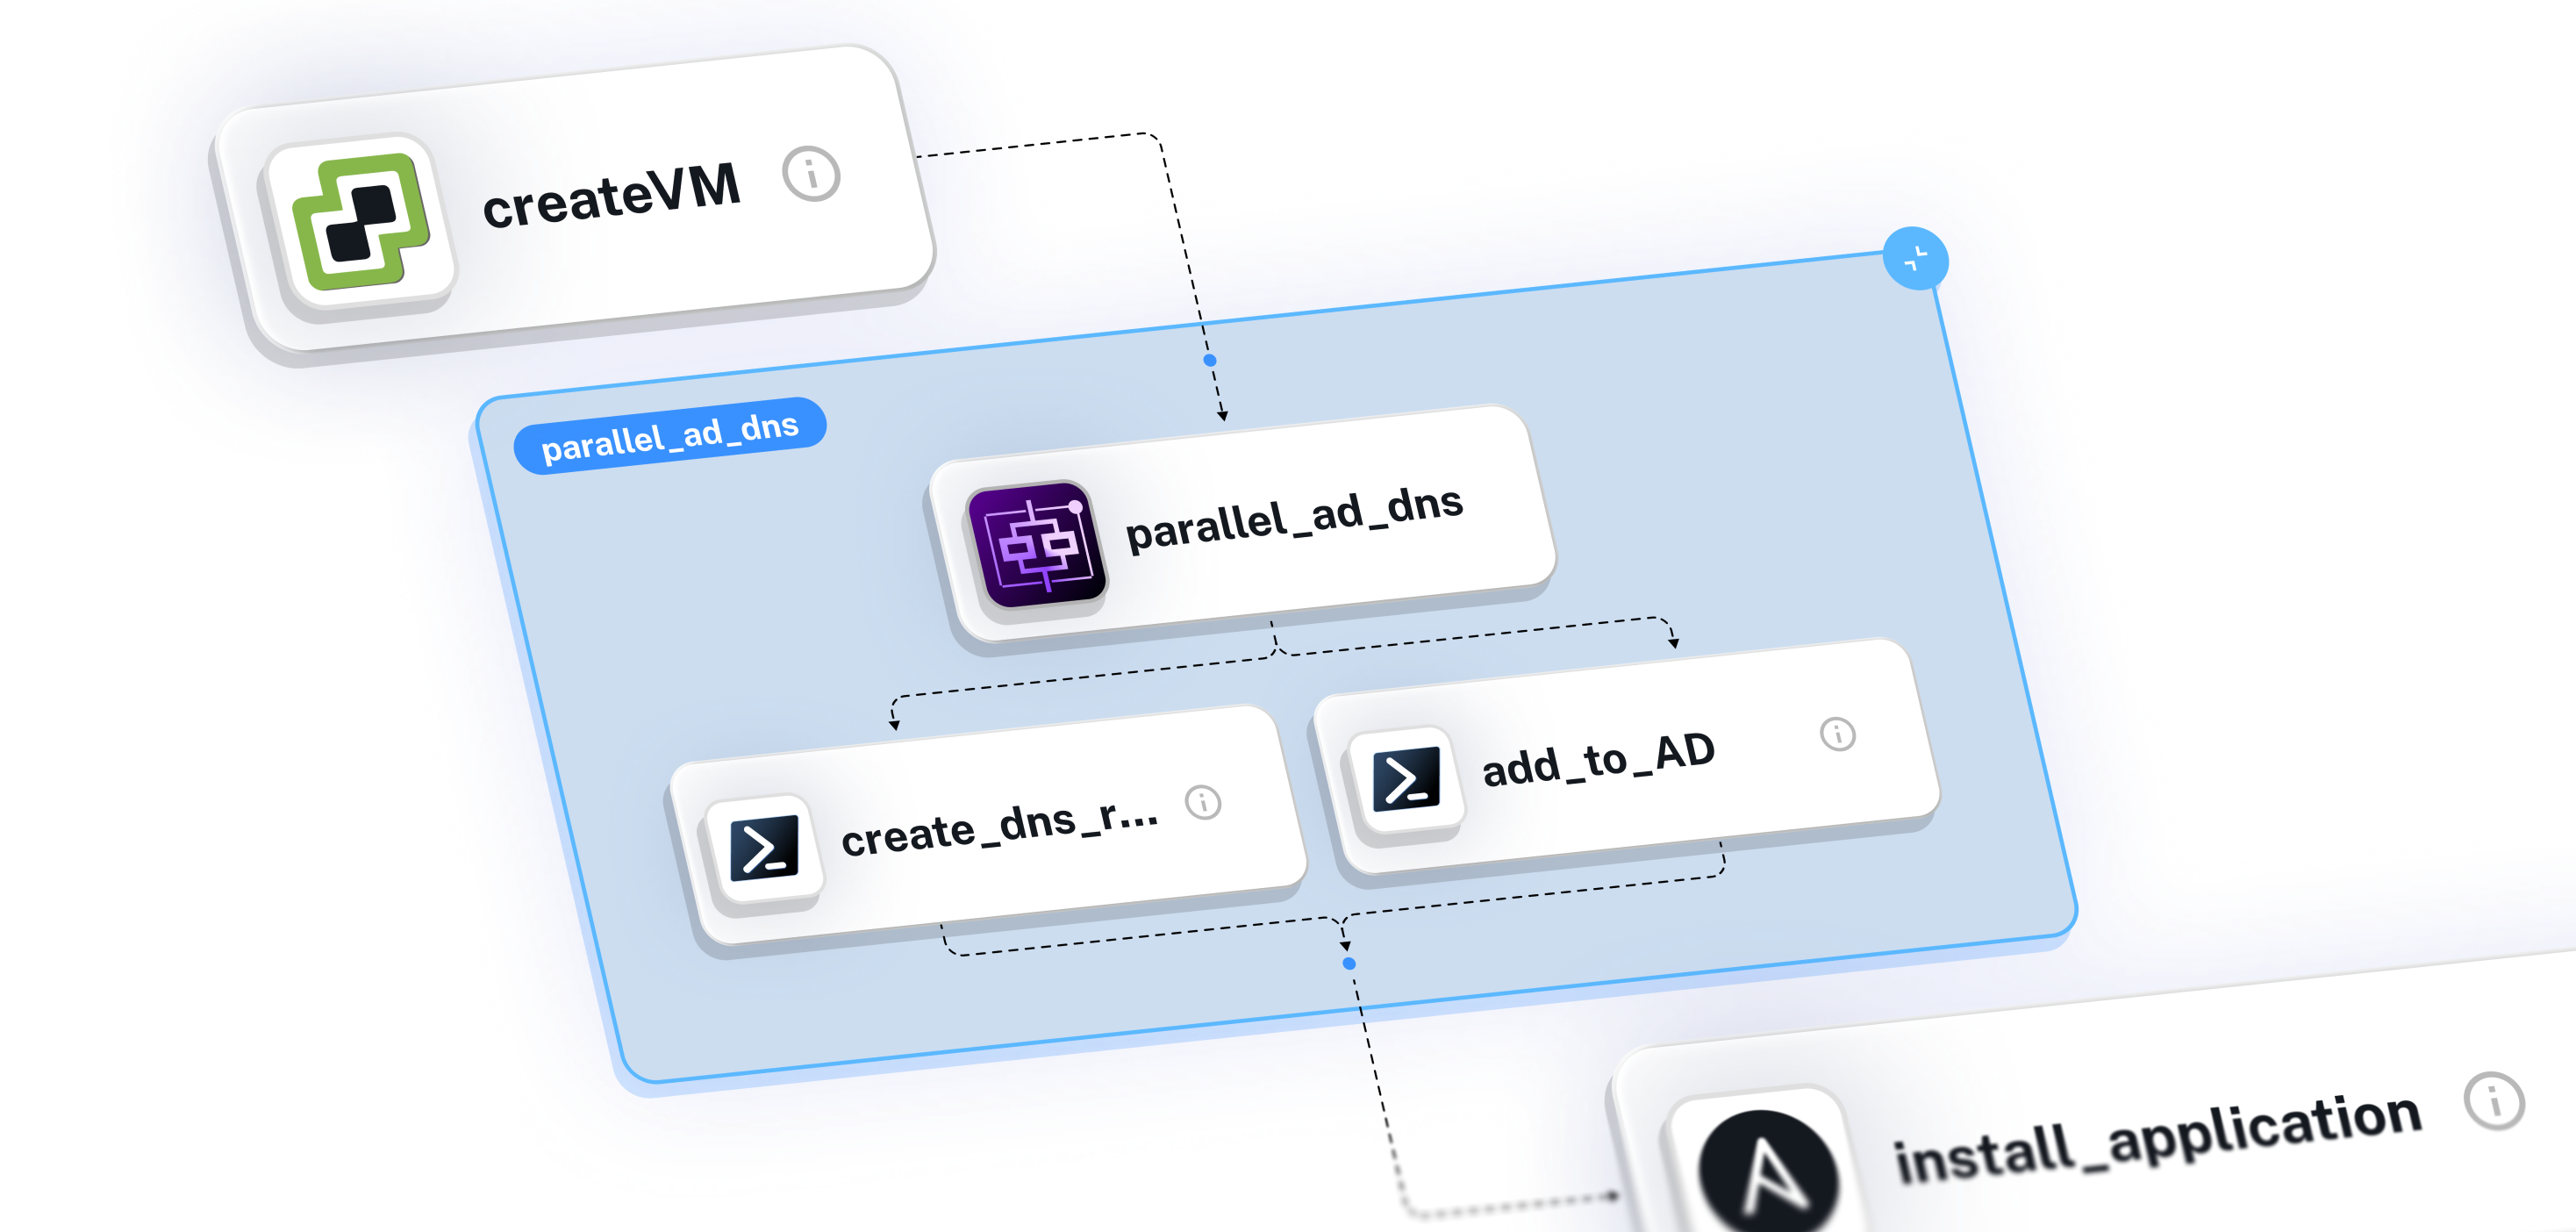
Provision and evolve workloads anywhere. Kestra workflows drive K8s, vSphere, cloud, and network APIs with consistent sequencing, execution, and traceability.
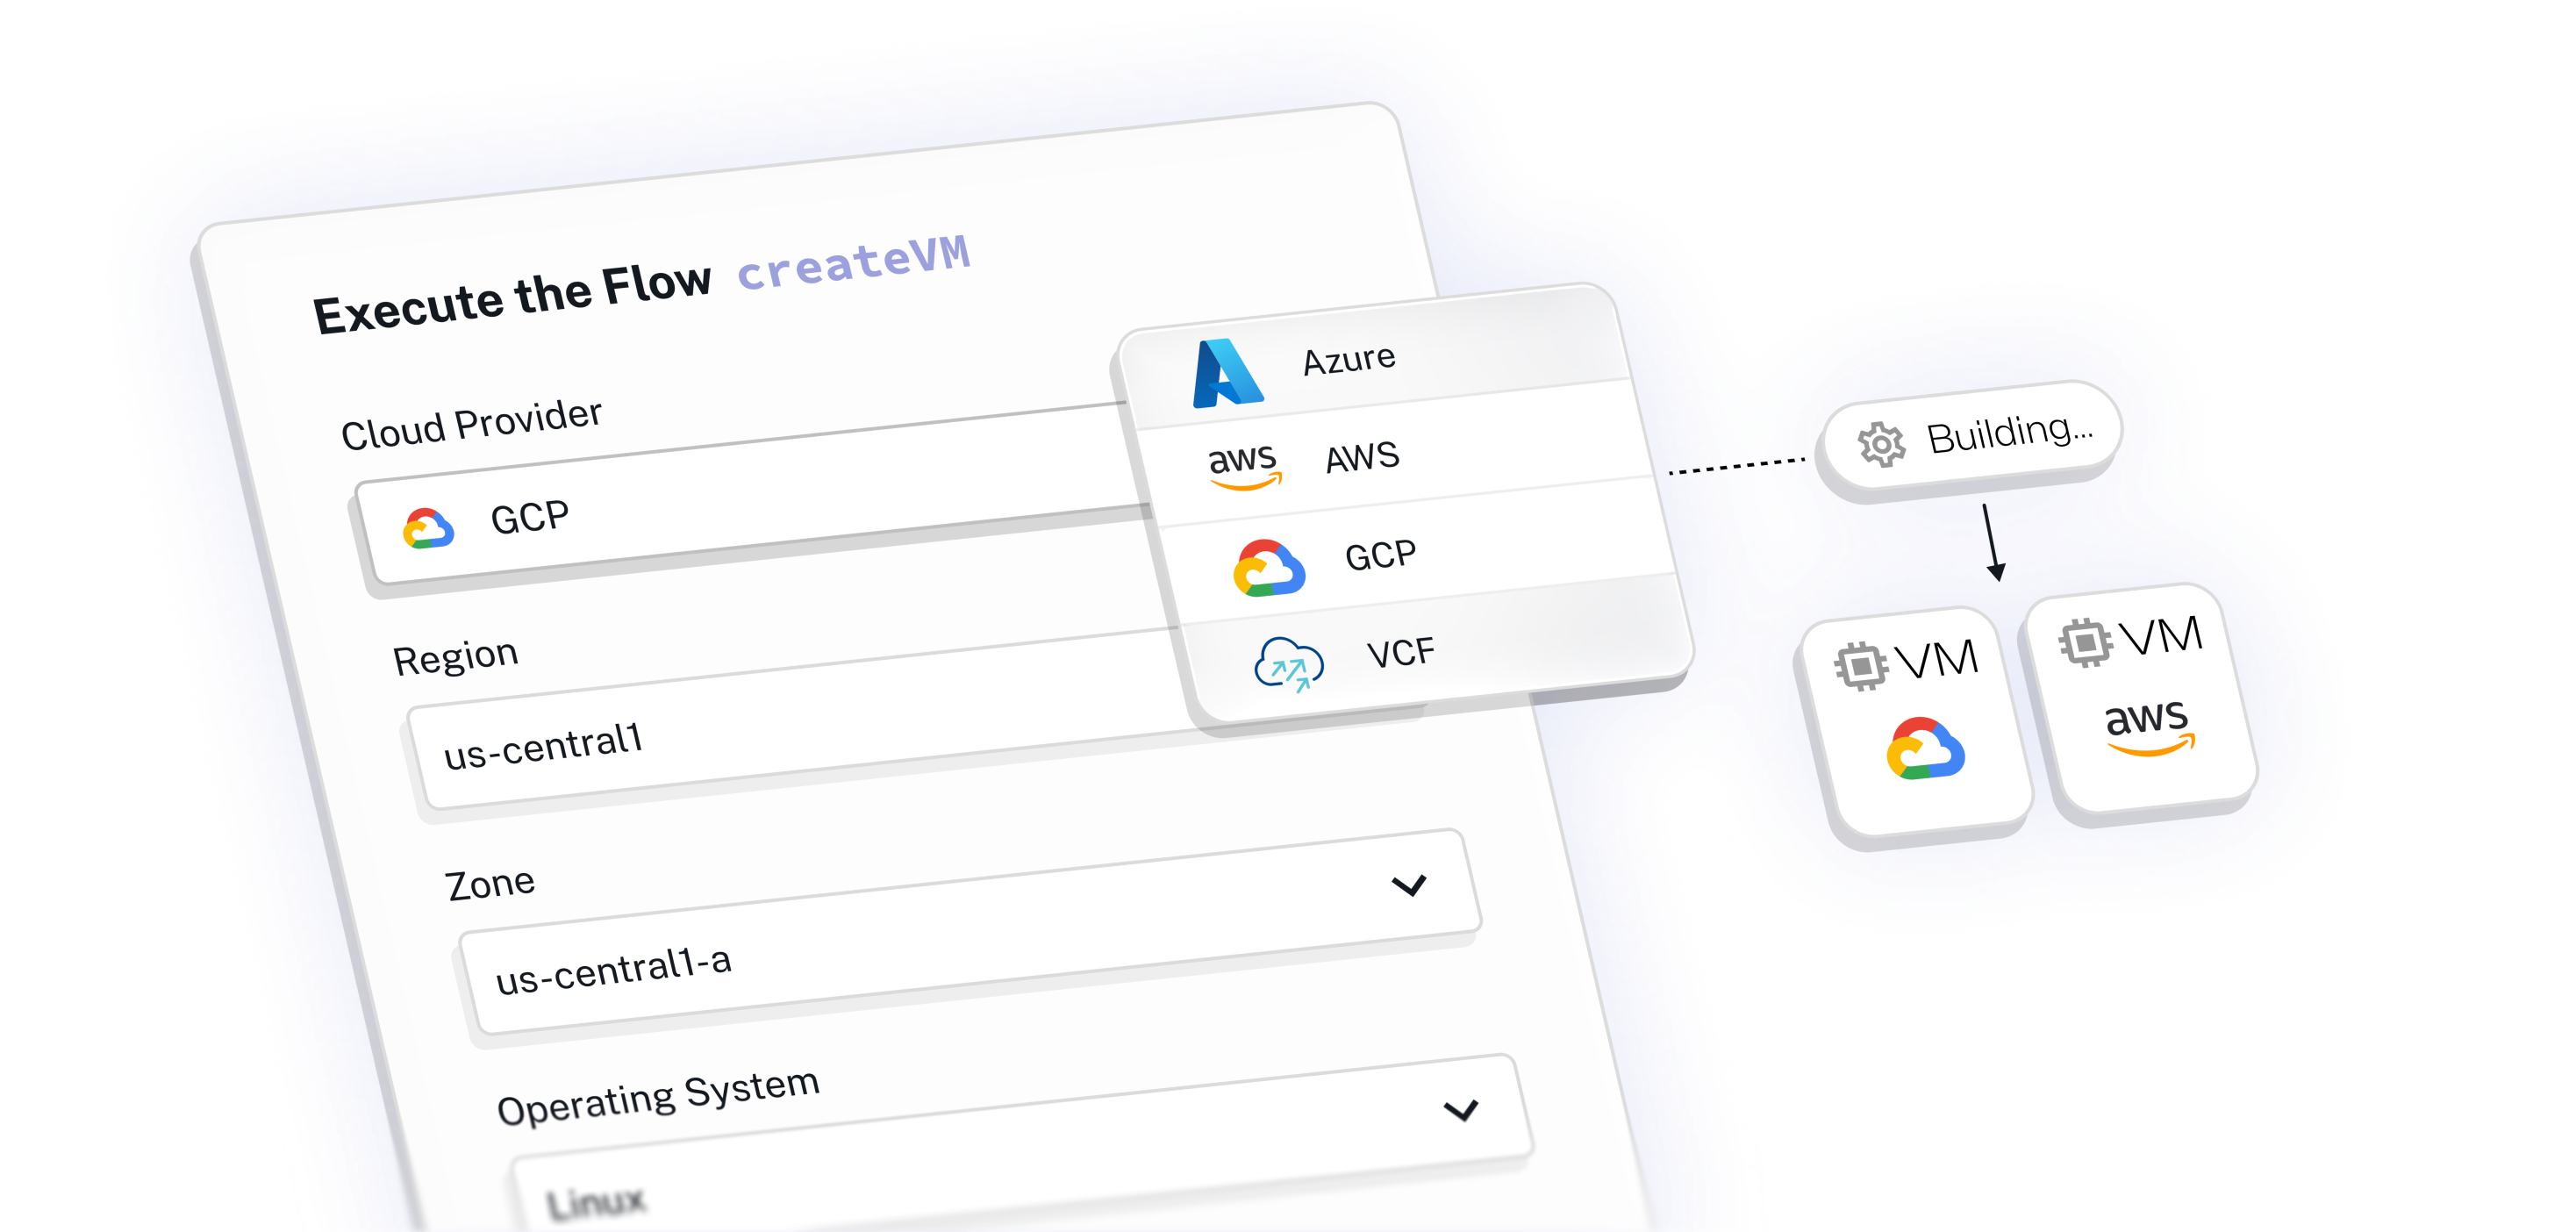
Pause workflows for critical checks. Kestra offers reliable Business Decisions with audit trail and controlled executions.
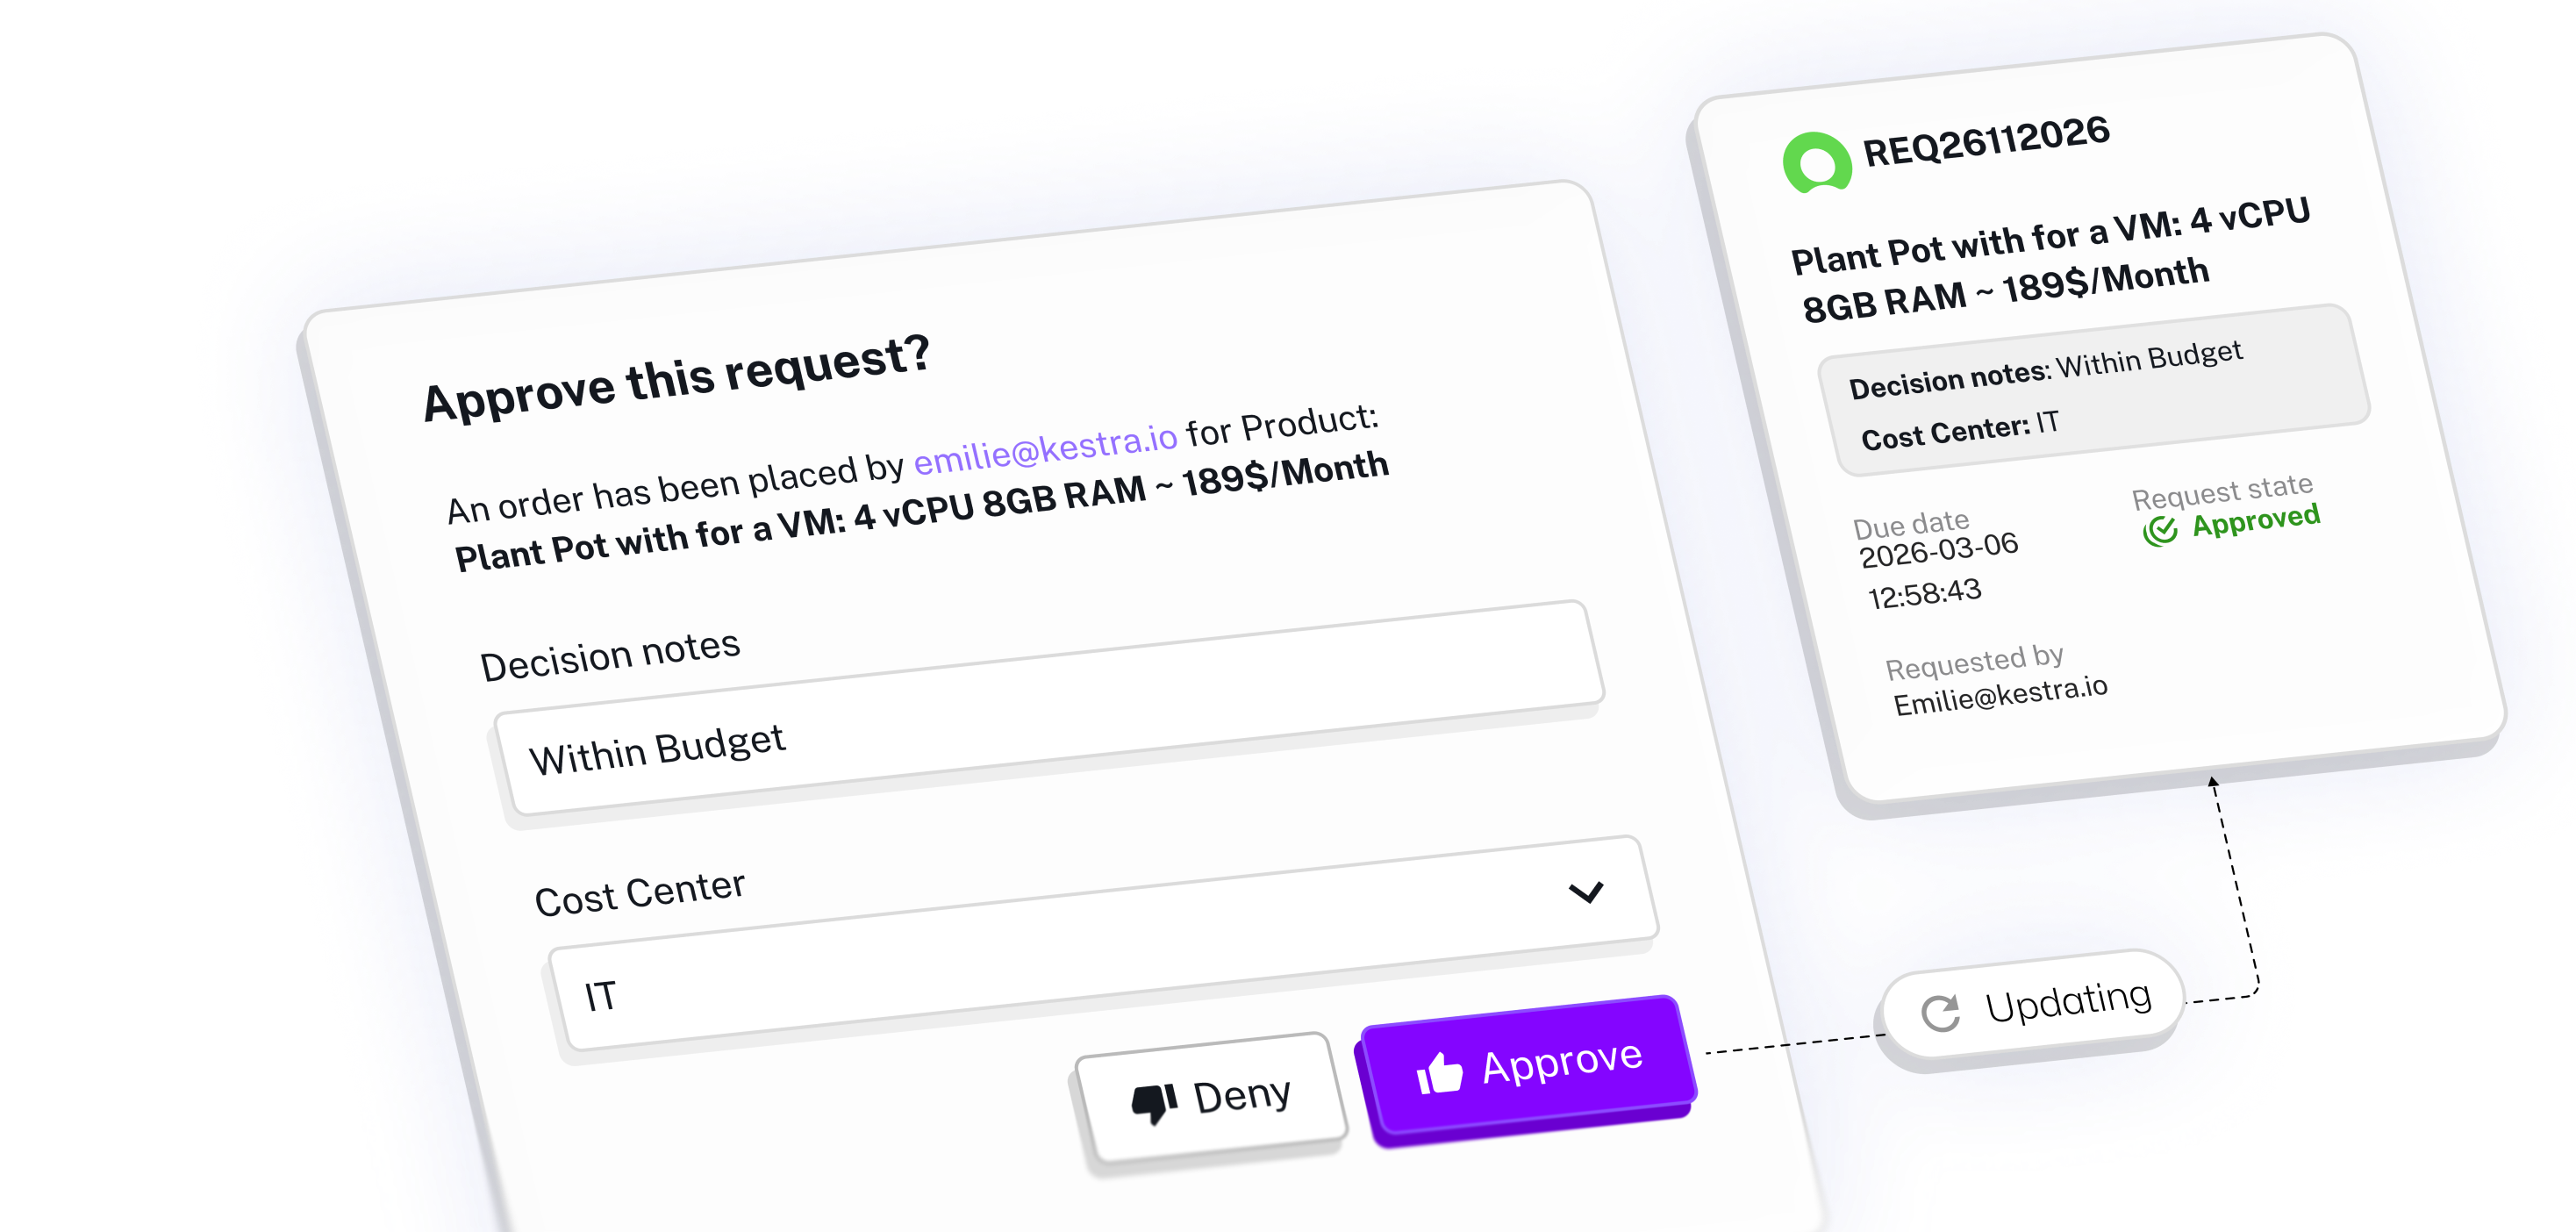
Wrap your playbooks in a production-grade layer. Gain structured inputs, secret injection, parallel execution, and granular logging without changing a single line of code.
Automate your Playbooks with KestraEnable true self-service infrastructure. Kestra turns catalog requests into provisioned resources, automatically updates the CMDB, and closes the ticket with audit proof, delivering assets in minutes, not days.
Manage your full ticket lifecycleExplore how Kestra gives you full control over complex infrastructure workflows.
Take the tour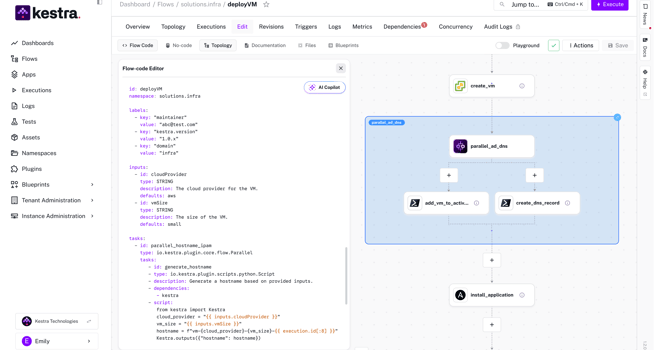
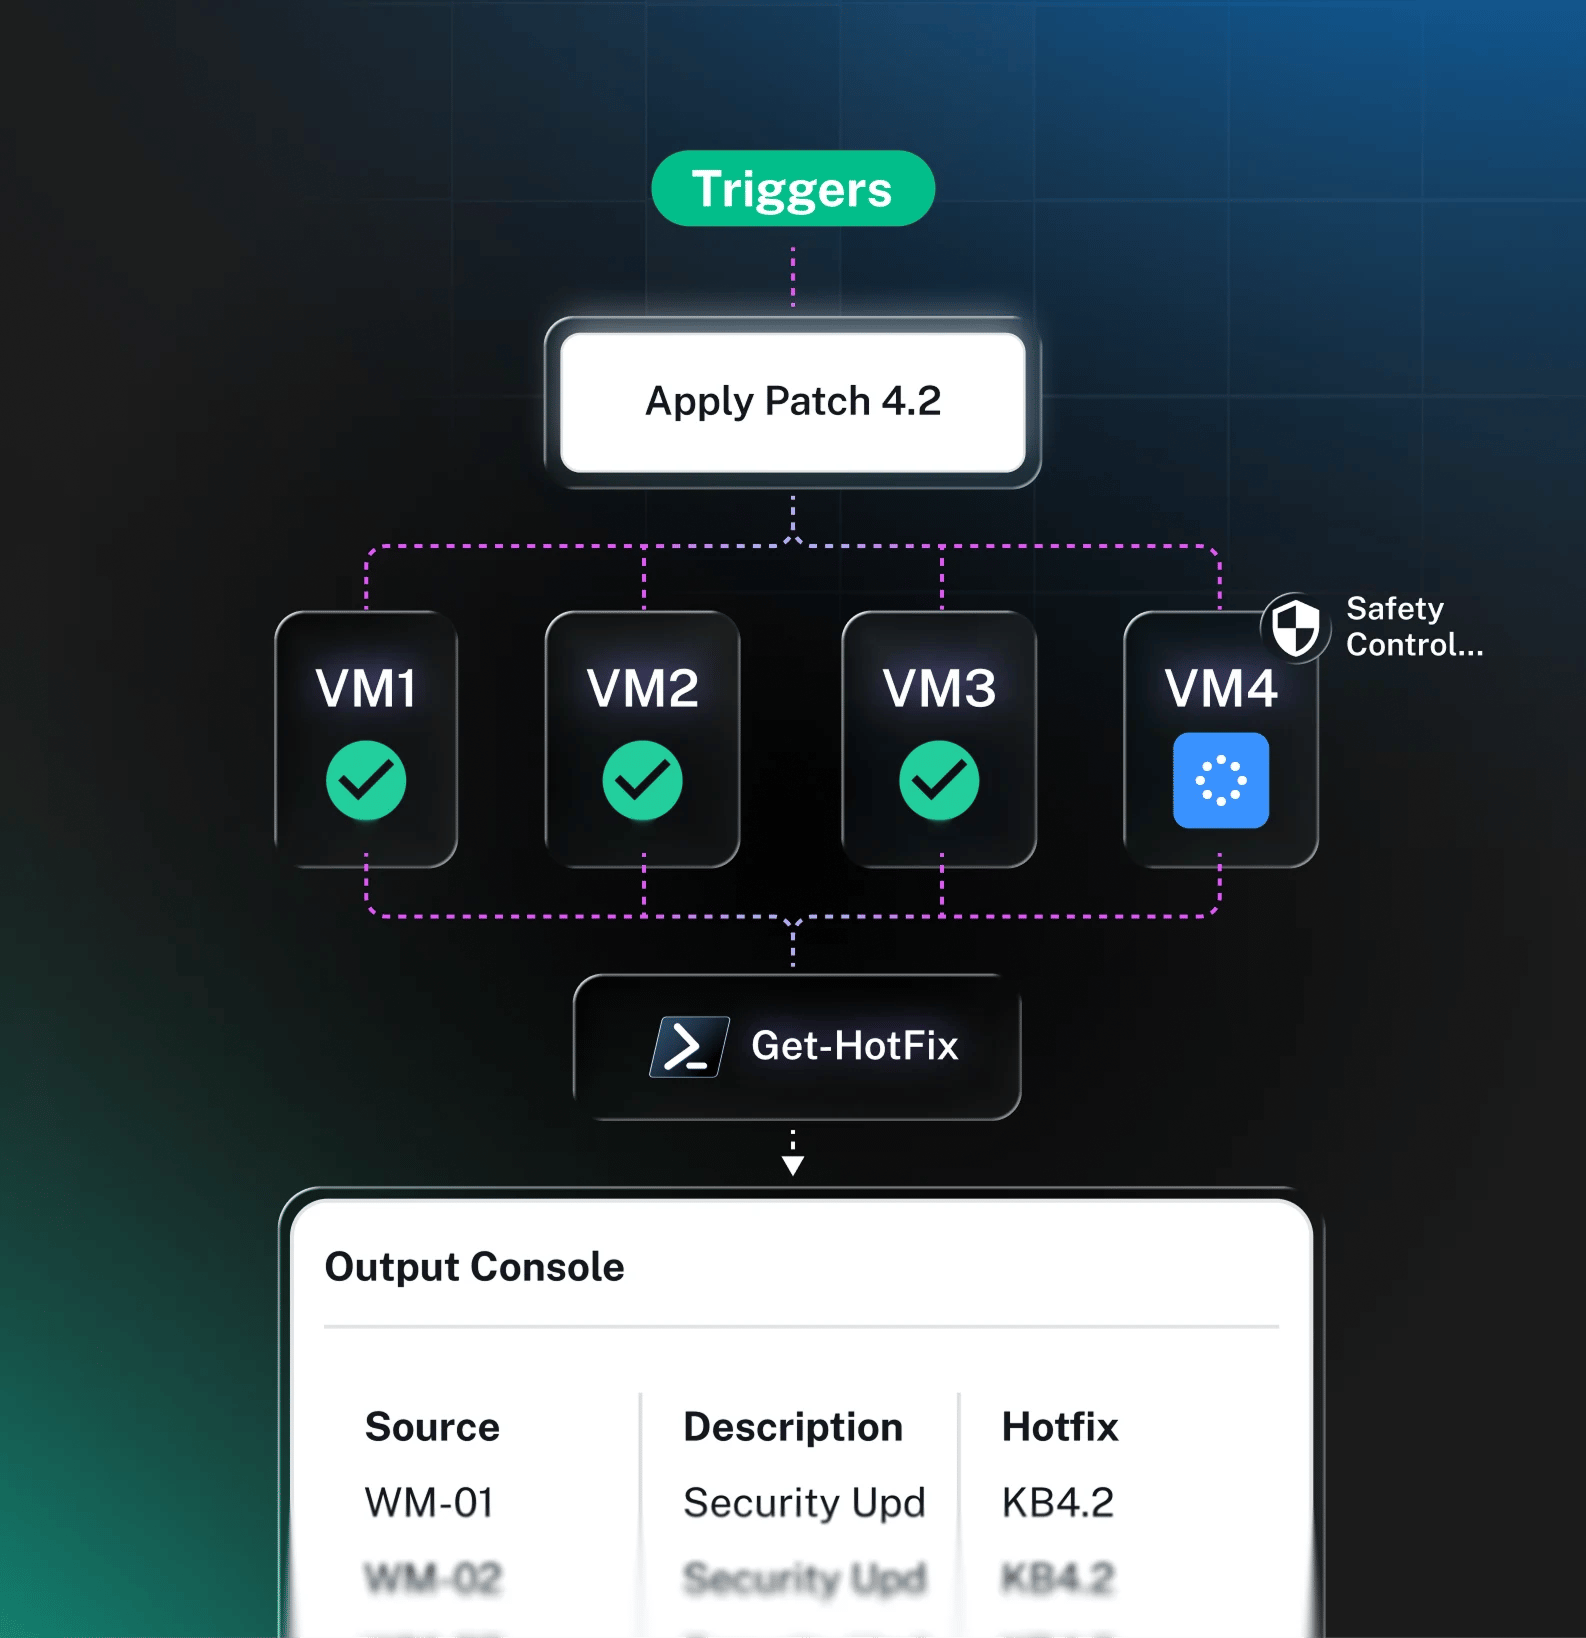
Orchestrate maintenance. Execute Ansible playbooks or PowerShell scripts across thousands of nodes with built-in safety controls.
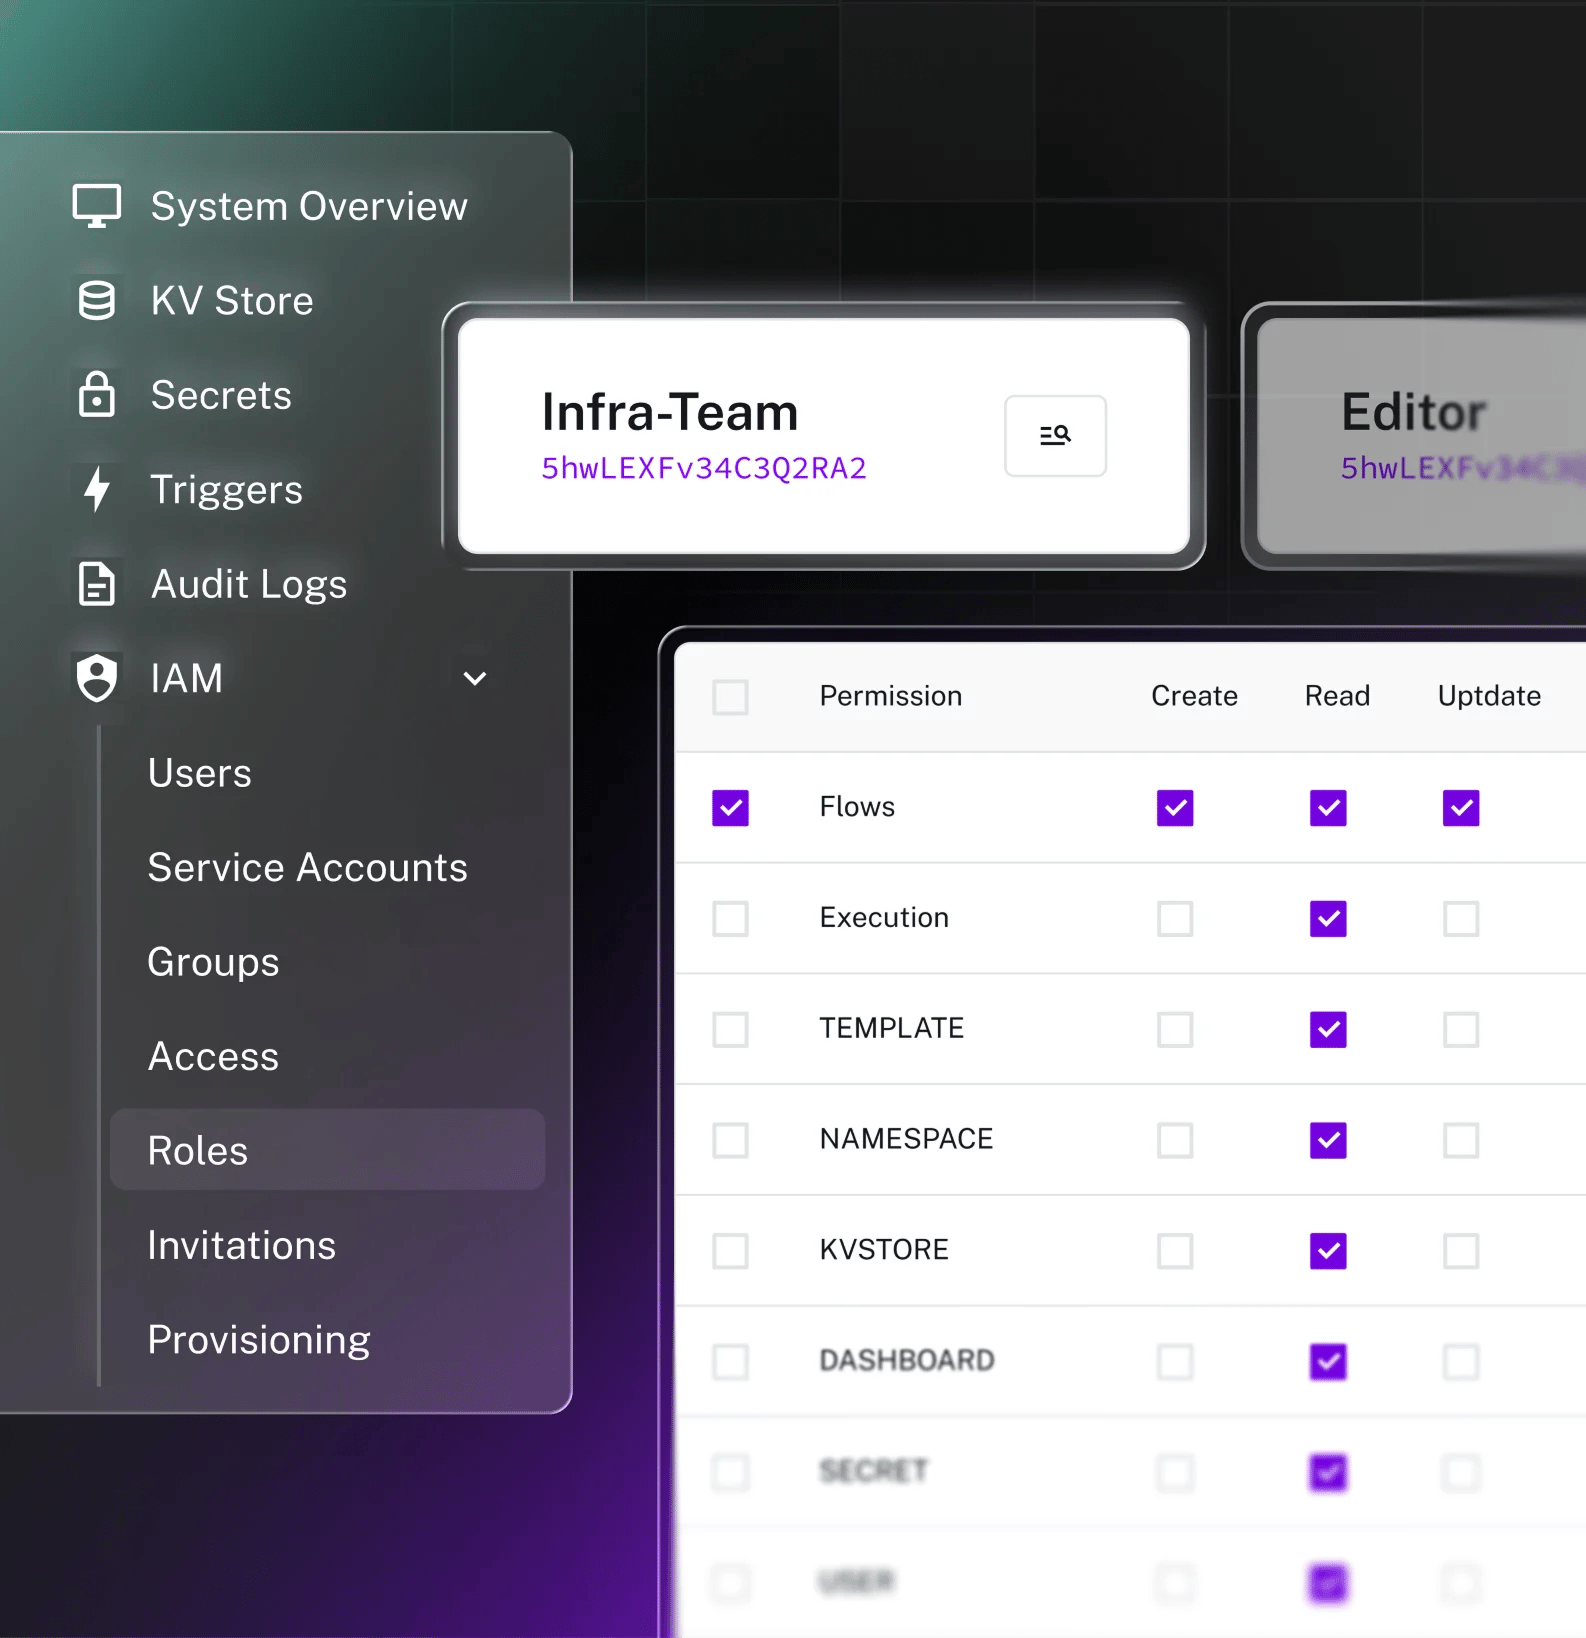
Enforce policies and rotate credentials. Turn manual security tasks into auditable, automated workflows.
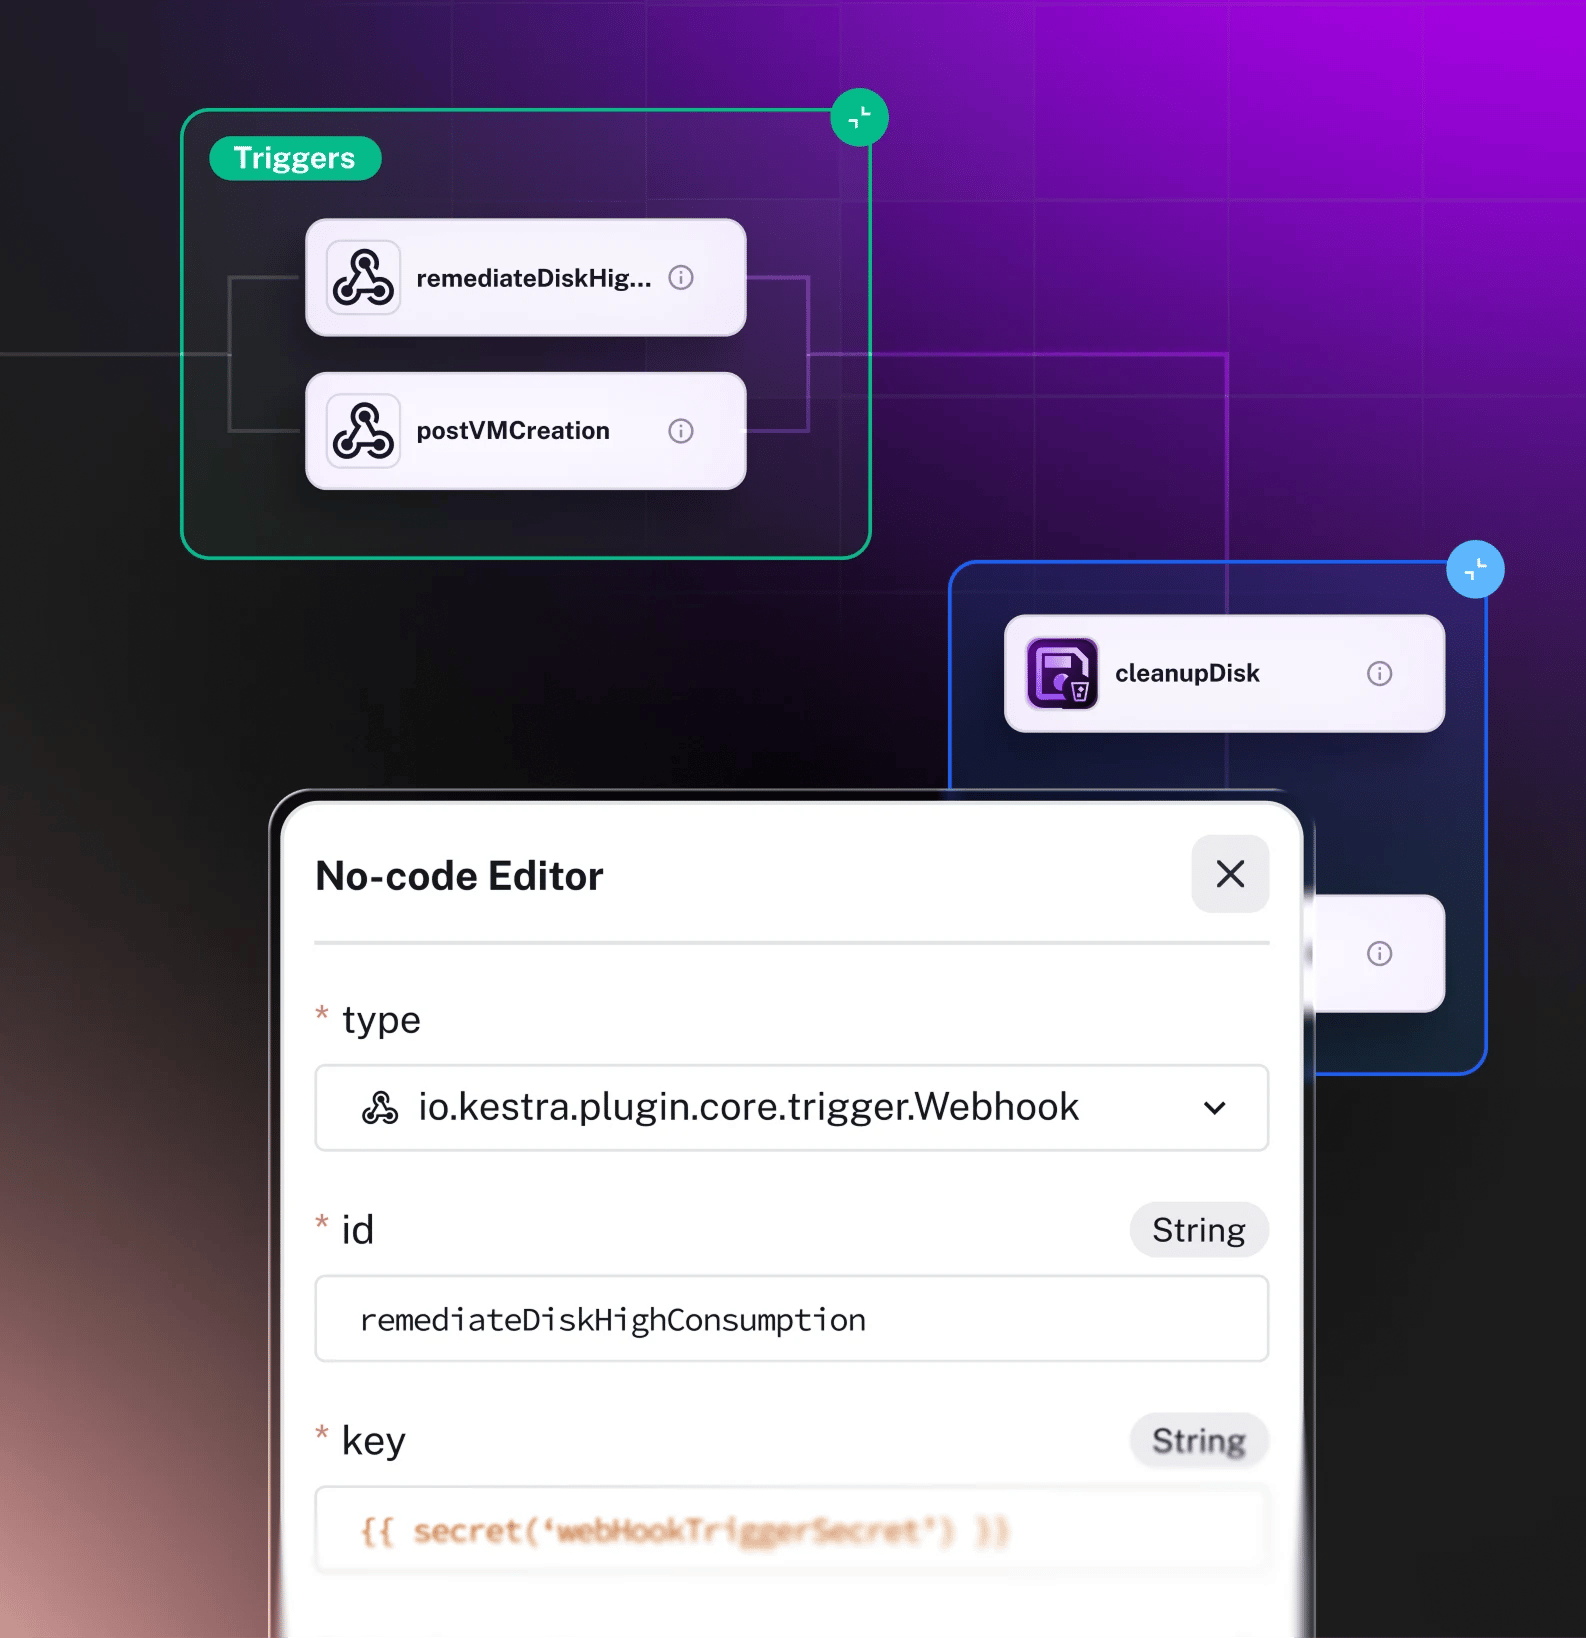
Reduce MTTR with event-driven logic. Connect your observability stack directly to remediation workflows.
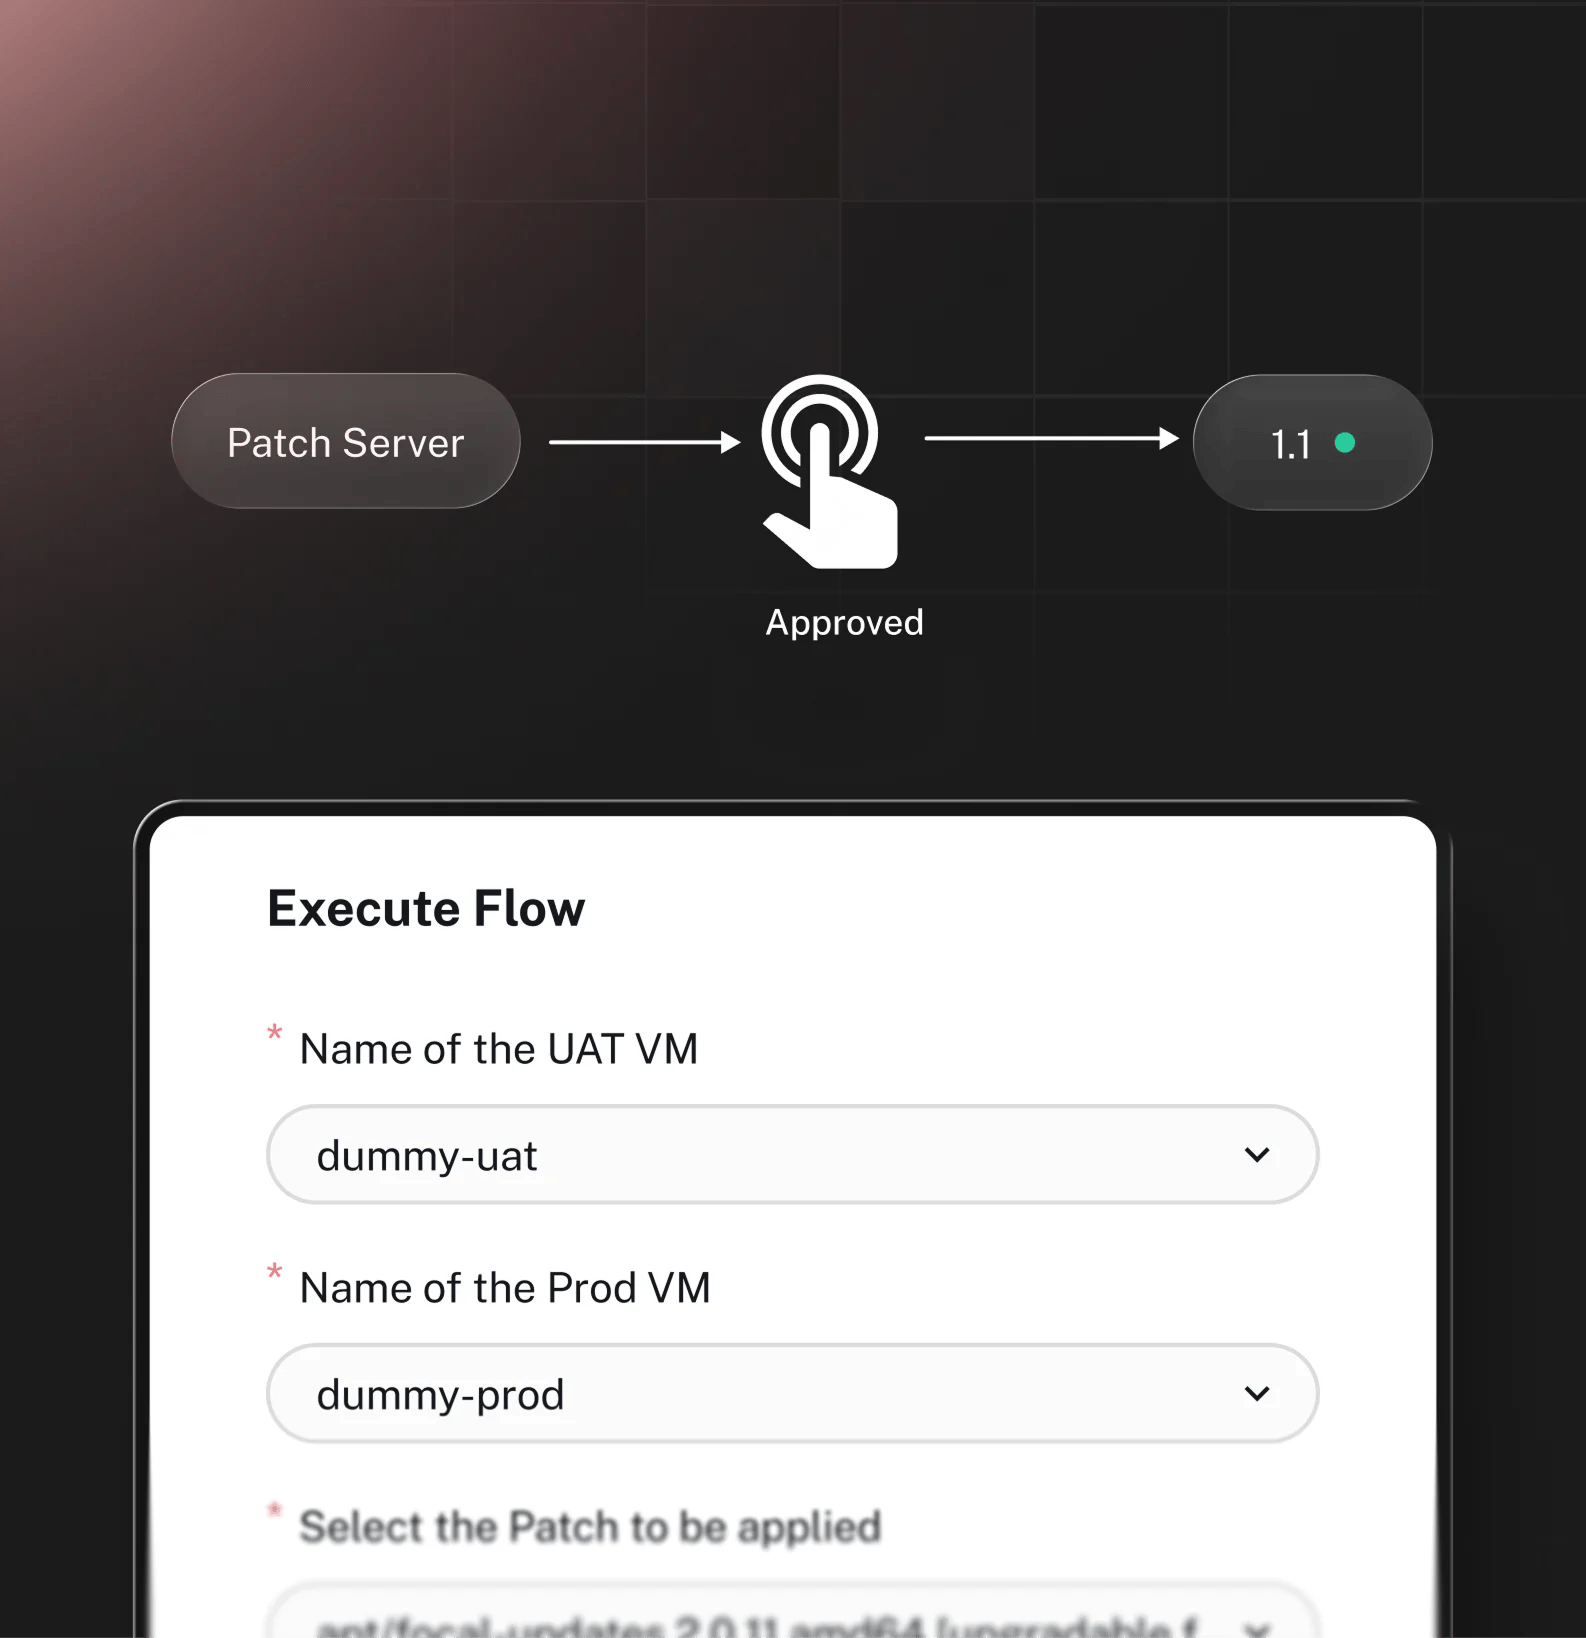
Wrap complex automation into interactive apps. Allow users to request resources or patching via simple forms, routing requests for human approval before execution.
Deletes ConfigMaps and Secrets no pod references and reports the cleanup on Slack.
Run conftest against rendered Kubernetes manifests from a CI webhook and escalate every failed rule as a GitHub issue and a Slack alert.


Audits HashiCorp Consul Raft consensus cluster leadership and voter quorum to prevent service discovery outages.
Reads /etc/os-release from each image you list, checks the distro on endoflife.date, and alerts Slack when an image runs an OS that is past end of life or about to be.

Periodically audit container images in any Docker registry for HIGH and CRITICAL CVEs using Trivy and send a formatted Slack digest.
Audits Project Contour ingress controller for Envoy xDS configuration NACKs, CDS sync delay, and proxy disconnects.


On every push, collect the last ten commit subjects, check them with the Conventional Commits pattern, and escalate any violation to GitHub and Slack.
In-place container OS package hotpatching with SecOps approval gates and post-patch verification.


Every image pushed to your registry is scanned with Trivy. When OS packages have fixes, the execution waits for approval, Copacetic patches the image, Trivy scans it again, and the patched tag is published only if fewer fixable vulnerabilities remain.


Promote Kestra flows across tenants and environments automatically using the Kestra REST API on a schedule.

Audits Kubernetes CoreDNS for elevated DNS lookup request duration and upstream forwarder latency spikes.
Monitors Corosync high-availability cluster ring metrics to detect Totem token retransmission storms, node drops, and quorum loss.
Audits Cortex metrics storage for ingester ring unhealthy states, memory series overflow, and write flush errors.
Verify every image of a release with cosign against an allowed signer identity, pin each one to the verified digest, then publish or apply a digest-pinned Deployment.


Query a Cosmos DB container for documents that should have expired but are still present, classify the run by violation count, alert Slack, and optionally delete them and verify.


Catch Couchbase GSI indexes stuck in deferred or pending after a defer_build migration, build them behind a dry-run gate, then re-read system:indexes to confirm every one is online.


Find Couchbase keyspaces carrying two or more online GSI indexes on the same keys, condition and partition, keep one per group, then drop the surplus behind a dry-run gate and a human approval and re-read system:indexes to prove it landed.

Audit Couchbase GSI secondary indexes for offline, building, or degraded states with automated Slack alerts.
Find Couchbase N1QL requests whose elapsed time is over a threshold in system:active_requests, cancel each by requestId behind a dry-run gate and a human approval, then re-read system:active_requests and fail the run if any request is still over the threshold.

Scan a Couchbase collection for documents nearing TTL expiry and either log a dry-run triage report or quarantine them, with a Slack report per run.
Deletes ConfigMaps and Secrets no pod references and reports the cleanup on Slack.
Run conftest against rendered Kubernetes manifests from a CI webhook and escalate every failed rule as a GitHub issue and a Slack alert.
Audits HashiCorp Consul Raft consensus cluster leadership and voter quorum to prevent service discovery outages.
Reads /etc/os-release from each image you list, checks the distro on endoflife.date, and alerts Slack when an image runs an OS that is past end of life or about to be.
Periodically audit container images in any Docker registry for HIGH and CRITICAL CVEs using Trivy and send a formatted Slack digest.
Audits Project Contour ingress controller for Envoy xDS configuration NACKs, CDS sync delay, and proxy disconnects.

ServiceNow

Ansible

AWS

Azure

GCP

Git

Go

VMware
ServiceNow
Ansible
AWS
Azure
GCP
Git
Go
VMware
Your Unified Infrastructure Control Plane. From Terraform to Python, manage every tool and script in a single, governed environment.
Run tasks safely inside air-gapped networks, VPCs, and private data centers, or in the cloud of your choice.
Automatically capture full run history, task logs, approvals, and evidence bundles for instant compliance.
Manage infrastructure directly from a self service catalog. Kestra provisions the server, syncs the records, and resolves the ticket request automatically.
Reuse your existing scripts, Terraform modules, Ansible roles, alongside VMware, NetApp or any other tool you already use.
Keep your scripts lightweight. Offload inputs, secrets, retries, and backoff logic to Kestra, so your code focuses purely on the business logic.
Manage cloud, IT, and OT automation from one platform. Execute tasks securely inside your VPCs or private networks.
Workflows live in your codebase, move through CI/CD pipelines, and can be instantly rolled back if a deployment fails.

Teams replace vRO, Rundeck, Cron, Jenkins, and manual scripts with Kestra